Zelda: Ocarina of Time for Switch 2 leaks online hours after launch
The remake appeared on file-sharing networks the same day it released, with both the original build and a 23GB update already in circulation among those seeking unauthorized access.
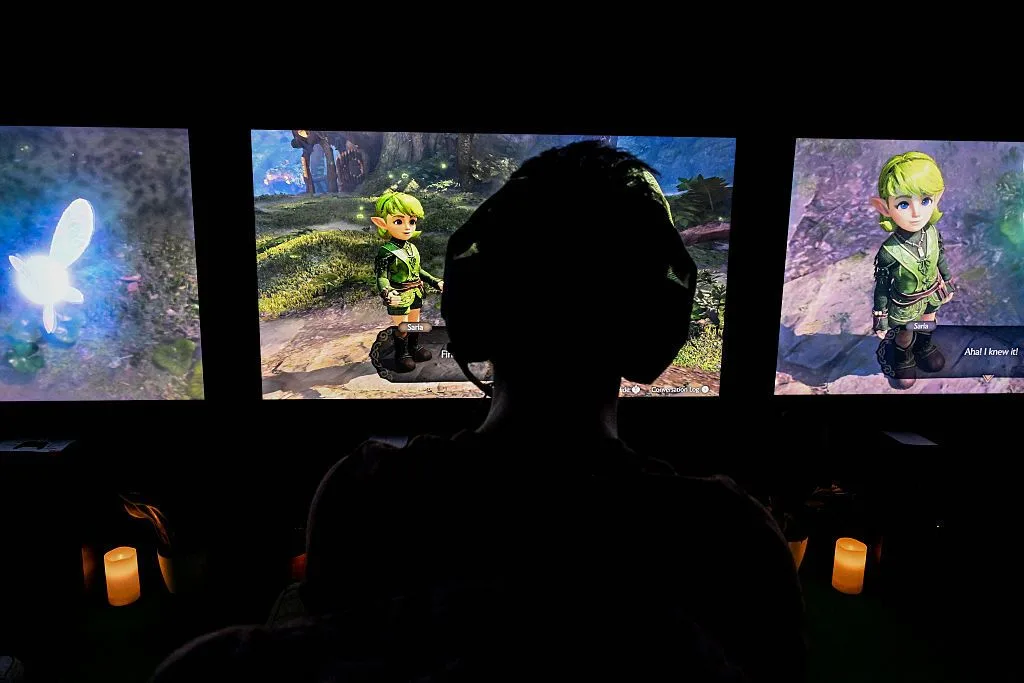
Nintendo's reimagining of The Legend of Zelda: Ocarina of Time surfaced on unauthorized distribution channels within hours of its Switch 2 debut. According to reports from a jailbreak community, both the initial 1.0.0 version and the subsequent 1.1.1 patch—which weighs 23 GB—are already spreading outside Nintendo's legitimate sales infrastructure.
The rapid proliferation follows a pattern established weeks earlier. Retail cartridges began arriving at consumer addresses several days before the official launch window, giving unauthorized users a head start. By November 1, gameplay footage had already surfaced across social platforms, with early adopters posting videos of themselves running the game. Despite this circulation, the title remains largely unplayable through PC emulation; graphics rendering issues plague most attempts, ranging from washed-out color palettes and blank screens to geometry clipping through environmental objects and crashes at the title screen.
Security researchers have identified the game by its title ID 0400486024DEC000 and traced the extraction to two software tools: ns2jb and OunceCake. The former represents a jailbreak developed by security researcher Sammy 'pepsipu' Hajhamid, who disclosed last month how he achieved code execution on Switch 2 without installing hardware modifications.
Hajhamid described the capabilities of his exploit in technical terms: "This lets us run homebrew, reverse engineer and mod Switch 2 games, back up save files off the Switch, and access most of the Switch 2's peripherals through MMIO. To my knowledge, it's the first such exploit for the Switch 2."
The exploit carries significant constraints that limit its utility. As a tethered jailbreak, it requires reactivation each time the console powers down. Additionally, it does not grant unrestricted kernel-level access. The same extraction methodology has reportedly been applied to Deltarune Chapters 1-4 and Mario Kart World.
This represents another chapter in an ongoing struggle between Nintendo and those seeking to circumvent its security measures. A day after Switch 2 launched in June 2025, an initial exploit emerged that permitted custom code execution but lacked root access or comprehensive jailbreak functionality. Nintendo has faced persistent challenges from cartridge backups as well. In August, the company issued seven Digital Millennium Copyright Act takedown notices that resulted in the removal of 401 GitHub repositories, including multiple Yuzu emulator forks.
Nintendo has remained silent regarding both the Ocarina of Time leak and the ns2jb exploit. However, SmileBASIC 4, the application used to trigger the jailbreak, vanished from the Nintendo eShop following the exploit's public disclosure.