OpenSSF and OpenBao Communities Converge at Prague Summit to Address AI Security Threats
The Open Source Summit Europe 2026 brought together OpenSSF ambassadors, maintainers, and operators to discuss surging vulnerability reports and the emerging security challenges posed by artificial intelligence.
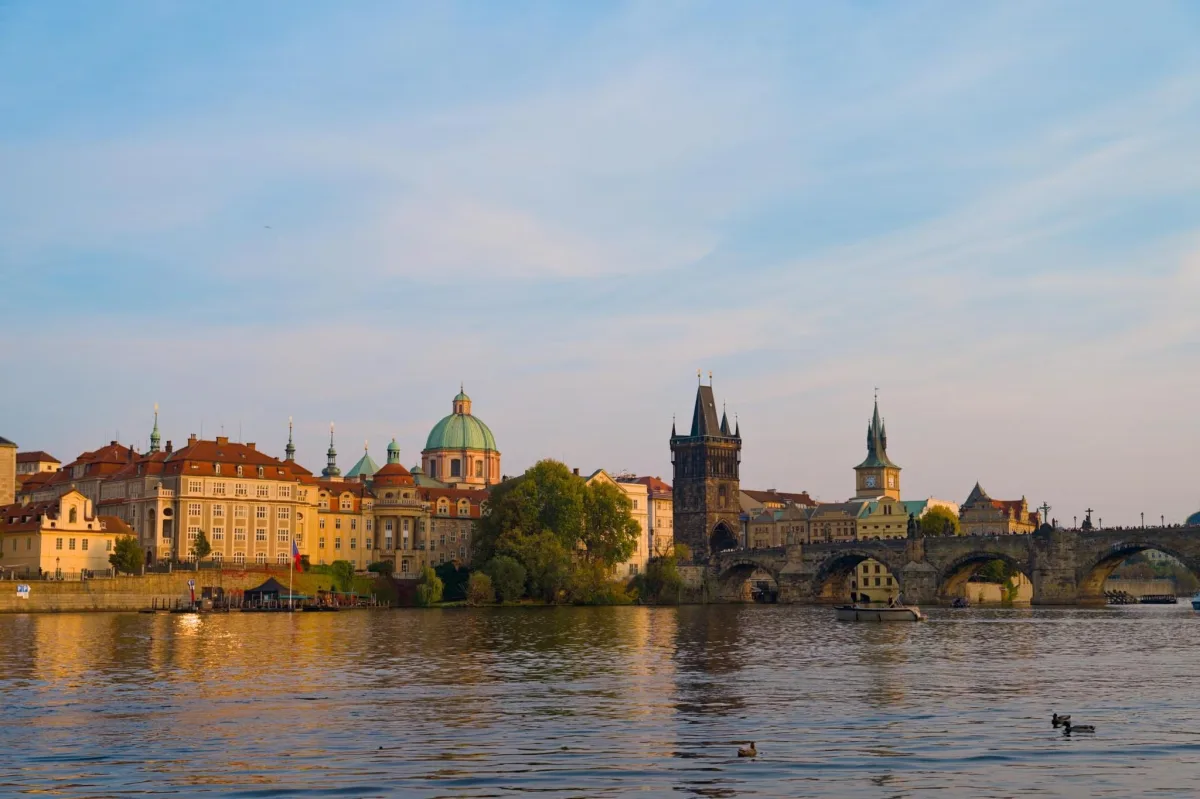
Community Gathering in Prague
Prague's Open Source Summit and its affiliated events served as a gathering point for the open source ecosystem, with newly appointed OpenSSF ambassadors taking prominent roles throughout the week. Hannah Braswell, Roman Zhukov, and Yunseong Choi delivered presentations at Tuesday's Community Day, while Kadi McKean, Katherine Druckman, and Zhukov also spoke at the main conference sessions. Staff from the OpenSSF, Technical Advisory Committee representatives, and community volunteers contributed talks across the program, including a return appearance of the Game Show featuring Christopher "CRob" Robinson and Adrianne Marcum.
The OpenSSF exhibition booth became a hub for conversations ranging from first-time visitors to long-standing community participants. Attendees engaged with representatives about the foundation's work, while branded merchandise—including CRAFish plushies and glow-in-the-dark OpenBao stickers—proved popular among visitors.
The conference's central moment came when Jamie Thomas delivered a keynote address examining how the OpenSSF and the newly launched Akrites initiative are equipping communities to defend against security threats emerging from next-generation artificial intelligence systems.
Bridging Fragmented Conversations
Like Prague's historic bridges connecting the city's divided geography, the summit functioned as a meeting place for disparate strands of the open source community. OpenBao participants from ControlPlane and other organizations mingled with representatives from ecosystem partners including SAP, Ericsson, Percona, Sylva, and the NeoNeophos foundation. Notably, OpenBao users from healthcare, energy, and financial sectors across Europe, Asia, and the Americas approached the OpenSSF booth to share experiences deploying the technology in corporate environments and laboratory settings.
Parallel discussions at the event reflected interconnected challenges facing different constituencies. Thomas's keynote addressed the explosion in vulnerability disclosures and Akrites' role in managing them, while booth conversations explored identifying weaknesses through OSS-CRS and examined how financial institutions are approaching the patching challenge using OSERA, a framework discussed by Gabriel Columbro of FINOS and Francesco Beltramini of ControlPlane. Maintainers grappled with processing surging vulnerability reports while meeting obligations under the European Union's Cyber Resilience Act, operators sought guidance on patching strategies, and organizational leaders assessed emerging trends and their implications.
Data released by the OpenSSF in partnership with Linux Foundation Research underscored the urgency of these conversations. The 2026 CRA Readiness Report documented a 394 percent year-over-year increase in CVE discoveries during the first quarter of 2026, with high-severity vulnerabilities climbing 811 percent across more than 14,000 open source projects. Participants widely anticipated this trajectory would persist and potentially accelerate.
Conference Sessions and Workshops
At the main conference, Adrianne Marcum and CRob examined artificial intelligence-generated content and emerging security challenges in their presentation titled AI Everywhere, Trust Nowhere. Madalin Neag participated in an October 9 workshop on operationalizing the Cyber Resilience Act alongside Roman Zhukov, Daniel Appelquist, and Megan Knight. Neag also presented separate sessions on Open Source Security as the Foundation of European Sovereignty with Mirko Boehm, and on CRA Compliance Paths and Where the Real Responsibility Sits.
OpenSSF members organized additional programming including a panel on SBOM quality featuring Takashi Ninjouji, Yoshiyuki Ito, Kiyoshi Owada, Tsukasa Yobo, and Yumi Tomita; a session on AI-assisted CVE triage led by Kazuyoshi Akiyama and Takashi Ninjouji; a discussion of regulatory intent and operational reality through ORBIT Launchpad presented by Rao Lakkakula and Sarah Evans; and an assessment of the NPM ecosystem's health by Adam Herzog and Alyssa Wright, alongside numerous presentations from community newcomers.
Upcoming Events and Resources
The OpenSSF will host SecurityCon during KubeCon North America on November 9th, followed by next year's Open Source Summit North America in Vancouver, BC. Those seeking additional information can explore the OpenSSF's calendar of upcoming events and subscribe to its newsletter for regular updates between conferences.
Recordings of presentations from Open Source Summit Europe 2026 are now accessible through the OpenSSF channel on YouTube, organized into playlists covering both the Community Day and main conference sessions.