OpenSSF Launches Community Guide to Navigate EU Cyber Resilience Act Compliance
The Open Source Security Foundation has released a role-based resource journey to help open source maintainers, stewards, and manufacturers understand their obligations under the EU Cyber Resilience Act, which imposes its first reporting deadline on September 11, 2026.
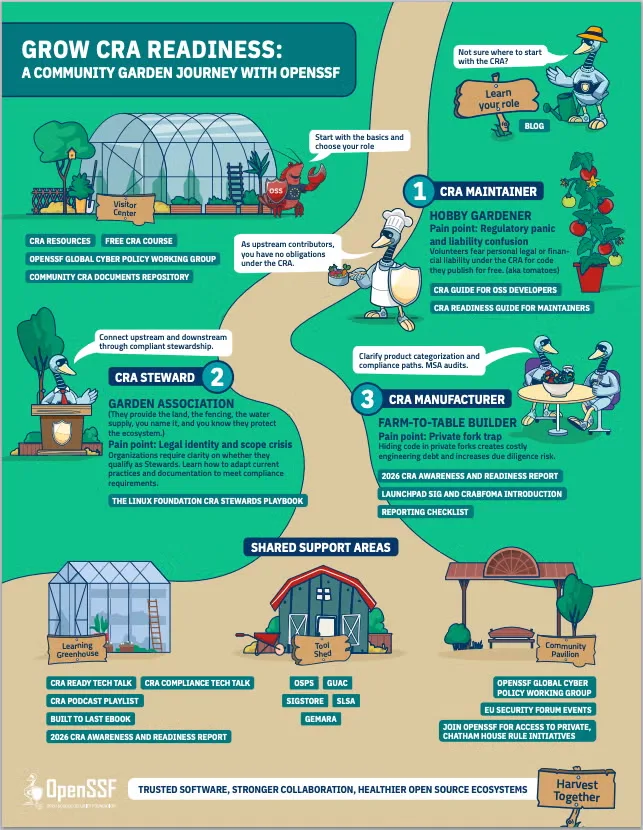
Uncertainty about how the EU Cyber Resilience Act applies to different participants in the open source ecosystem prompted the Open Source Security Foundation to develop a new navigation tool. The Grow CRA Readiness: A Community Garden Journey resource guides maintainers, open source software stewards, and manufacturers through their specific roles, legal obligations, and available compliance tools and support structures.
Questions about the CRA's scope and impact circulate widely across the open source community: Where does my organization fit? What actions must I take? Which resources address my particular responsibilities? OpenSSF created this journey to provide straightforward answers, allowing participants to pinpoint their role and access targeted guidance, tools, and community assistance.
Understanding the EU Cyber Resilience Act and its timeline
The EU Cyber Resilience Act establishes cybersecurity standards for hardware and software products distributed within the European Union market. The regulation's first significant milestone occurred on September 11, 2026, when manufacturer reporting obligations commenced. Broader compliance requirements take effect on December 11, 2027. Grasping one's role within this framework represents an essential starting point for any organization seeking reliable guidance.
How open source communities can prepare
Confusion about the CRA's applicability remains widespread. According to the 2026 CRA Awareness and Readiness Report, 66% of survey respondents lacked familiarity with the regulation. In response, OpenSSF prioritized Policy and CRA alignment within its 2026 community roadmap. Collaborating with the Global Cyber Policy Working Group and its Awareness SIG, the foundation developed the journey alongside podcasts, Tech Talks, written guides, and supplementary materials designed to help participants locate their position and proceed to the next stage.
The community garden framework for understanding CRA roles
The journey employs a community garden metaphor to illustrate the distinct roles within the open source ecosystem. In a conversation on the What's in the SOSS? podcast, Roman Zhukov explained that while everyone contributes to the garden's vitality, responsibilities vary by participant. This analogy became the structural foundation for the new resource.
Identifying your role under the CRA
Open source maintainers and contributors
Maintainers and contributors function as hobby gardeners, developing code and distributing it within the community. Those creating non-commercial open source software typically do not assume the manufacturer's CRA obligations. The journey directs these participants toward practical security practices that strengthen projects and benefit downstream users.
Open source software stewards
Stewards operate as the garden association, furnishing governance, support, and resources that enable projects to flourish. The CRA recognizes stewards as a distinct category with tailored responsibilities. The journey connects stewards with guidance tailored to their specific role.
Manufacturers of products with digital elements
Manufacturers serve as farm-to-table builders, taking components from the shared ecosystem and assembling them into products marketed under their own name or trademark. Manufacturers bear the most extensive CRA obligations. The journey directs product, engineering, security, and compliance teams toward resources supporting their preparation efforts.
Uncertainty about which category applies to your organization? Begin with the Grow CRA Readiness journey. An entity may pursue multiple pathways across different initiatives and offerings.
CRA reporting and compliance deadlines
Reporting obligations under the CRA commenced on September 11, 2026. The journey connects manufacturers and stewards with current reporting guidance and specialists who address these matters, streamlining access to relevant resources and information.
Full CRA requirements activate on December 11, 2027. Organizations need not address all requirements simultaneously, but should begin determining their role and establishing a roadmap. The journey simplifies this initial step and provides links to comprehensive guidance as requirements evolve.
Integration with OpenSSF's Lazy River journeys
OpenSSF's Lazy River user journeys assist software developers, security engineers, OSPO leaders, marketing and community professionals, and executives in locating OpenSSF projects and communities relevant to their work. The CRA community garden journey introduces a regulatory dimension to this framework.
The Lazy River addresses the question, "Where do I fit in OpenSSF?" The community garden addresses, "What role do I play in CRA readiness?" Most participants will find value in both resources. A security engineer employed by a manufacturer, an OSPO leader defining stewardship, or an executive developing a compliance strategy can follow a professional journey and the CRA role-based path concurrently.
OpenSSF's CRA readiness resources
The journey consolidates community resources into four accessible locations:
- The visitor center houses the OpenSSF CRA resource hub, training materials, guides, and the Built to Last eBook.
- The learning greenhouse contains the CRA Readiness Tech Talk, podcast series, and CRA readiness research.
- The tool shed references OSPS Baseline, SLSA, Sigstore, GUAC, and Gemara.
- The community pavilion links readers to the OpenSSF Global Cyber Policy Working Group, its public meetings, SIGs, Tech Talks, and community resources.
Visiting every location at once is unnecessary. Select your path, retrieve the resource you require today, and return as your circumstances develop.
Getting started with CRA readiness
Begin by exploring the journey itself. Determine your role, follow your designated path, and leverage the OpenSSF community to advance to the next phase. While CRA readiness presents genuine challenges, participants need not navigate them in isolation.
This article serves informational purposes and does not constitute legal advice. Consult current official guidance and your legal or compliance advisers regarding your particular situation.