French Blood Banks Hit in Wave of Refrigeration System Attacks
Hackers targeted cooling units operated by France's blood service following a series of cyberattacks on supermarket freezers, though staff prevented any loss of stored materials by moving them to safety.
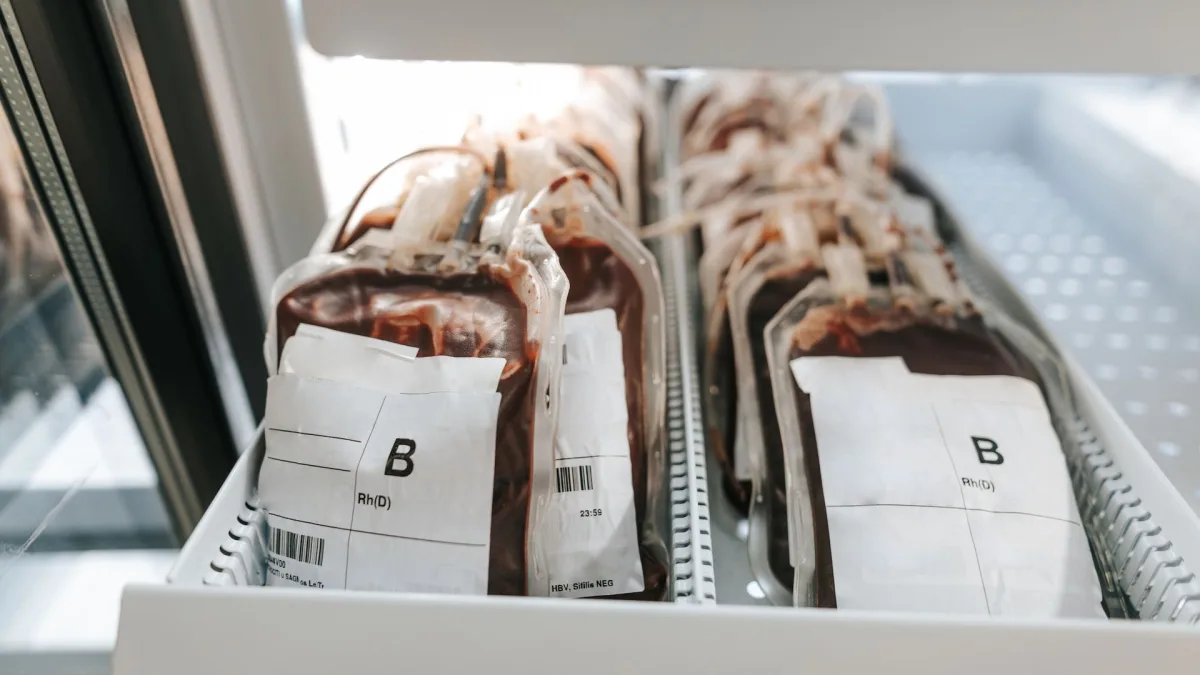
A fresh round of cyberattacks has struck refrigeration equipment across Europe, this time targeting units managed by the French blood service, known as the EFS. The intrusions came on the heels of earlier compromises affecting supermarket freezer systems. The EFS confirmed that no biological materials were compromised, as the organization's monitoring systems detected the breach and prompted personnel to relocate affected inventory to secure storage.
France's Health Ministry indicated it is tracking the situation closely and that no resources were lost in the incident. The breach appeared to concentrate on refrigeration systems at three separate locations, with the Burgundy-Franche-Comté region identified as one target. According to the EFS statement, the intrusion occurred through a service provider, widely reported to be Coolworld.
Coolworld released a statement attributing the breach to "remote monitoring software" operating within its infrastructure, specifically citing "a component from a third-party supplier" as the source. Technical specifics remain unavailable, leaving unclear whether attackers accessed internet-exposed equipment as they did during the supermarket incidents, or whether they first penetrated Coolworld's internal network to reach the controllers.
Notably, it was the EFS' own monitoring and alert infrastructure that identified the compromise—not the vendor's detection systems. This distinction underscores a potential gap in the vendor's security posture.
Vendor-Specific Vulnerabilities
The ongoing campaign appears to target refrigeration controllers on a vendor-by-vendor basis. Danfoss has emerged as the most frequently cited manufacturer, particularly in attacks occurring November 1-2. Earlier intrusions on October 13-14 involved Copeland/Dixell controller units.
Danfoss documentation recommends deploying its controllers behind "appropriately configured firewalls and secure LAN," explicitly advising against placement on public or unsecured networks. The company issued a support bulletin in October 2026 explicitly mandating VPN protection, though earlier documentation does not appear to contain this guidance based on available records. Such recommendations carry limited practical value when firewall exceptions effectively expose systems to external access.
Copeland/Dixell manuals for the affected controller models instructed installers to route ports 80 (HTTP) and 22 (SSH) to the internet to enable remote access, presenting VPN as merely an optional measure. Following the initial wave of attacks on October 14, the company released a security advisory reversing this guidance and restricting access to VPN-protected connections only.
Attribution and Motivation
Multiple news organizations reported seeing materials—posted to Telegram before deletion—in which Russia-aligned hacking collectives Noname057(16) and Z-Pentest claimed responsibility for the attacks. Z-Pentest allegedly published 2,500 lines of Danfoss source code, though none of these materials have surfaced publicly. The purported attackers characterized their actions as exposing inadequate cybersecurity practices.
While some observers point to autonomous AI systems as emerging threats in cyberattacks, the pattern here mirrors historical precedent: the tools themselves primarily expose existing security deficiencies and accumulated technical debt rather than creating entirely new attack vectors.