Nine-Year Xbox 360 Exploit Finally Simplified With $4 Microcontroller
A modder has completed a long-standing voltage glitch modification for the Xbox 360 using only a Raspberry Pi Pico, demonstrating how specialized hardware exploits can be replicated with commodity components.
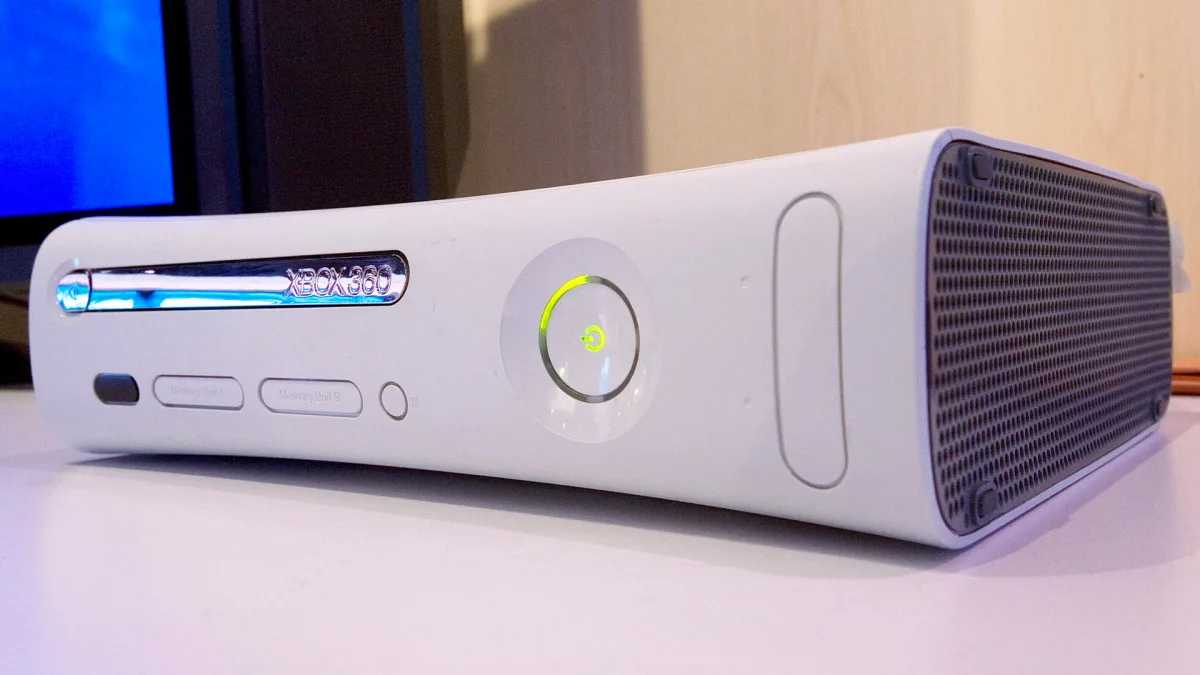
Microsoft's gaming console has faced repeated security breaches throughout its lifecycle, with the company typically closing each vulnerability through firmware updates. The first successful crack involved modified DVD firmware released in 2006, followed by a hypervisor vulnerability in 2007 and a JTAG debugging port exposure discovered in 2009. Among these various attack vectors, the 2011 CPU force-reset exploit proved to be the most resilient, originally demanding specialized hardware and dedicated glitch chips to execute.
A recent development shows that this persistent exploit can now be performed using a Raspberry Pi Pico microcontroller, available for approximately $4. While a soft-mod technique called PeerPressure was released just last week for the Xbox 360, the focus here remains on the hardware-level approach involving direct signal manipulation.
The reset exploit functions by transmitting a precise signal into the CPU's reset pin. Rather than triggering the expected reset behavior, this manipulation causes the processor to execute its current instruction incorrectly, creating the conditions necessary to bypass the console's security mechanisms.