Ledger Overhauls Supply Chain Security After $93 Million Cryptocurrency Theft
Following a major supply chain attack that resulted in $93 million in stolen cryptocurrency, the hardware wallet maker is scrutinizing its sales channels and anti-tampering measures.
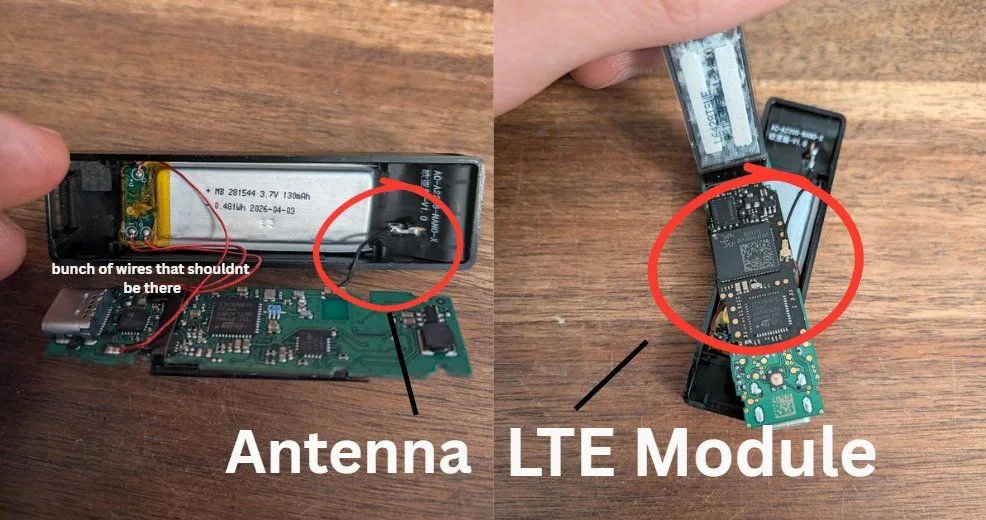
Ledger is conducting a comprehensive review of its distribution channels and customer acquisition methods in response to the "Cryptobilis incident," a supply chain compromise that enabled physical tampering of its devices and led to $93 million in cryptocurrency losses from user accounts. Bloomberg reported the incident on October 13, prompting the company to examine how its hardware wallets move from manufacturing through to end users.
Charles Guillemet, the company's chief technology officer, announced via social media that Ledger is also evaluating the anti-tampering safeguards built into its hardware. He instructed users whose signing devices had been compromised to reach out to Ledger's support team for return shipping details. Guillemet additionally provided guidance to users interested in manually inspecting their devices for signs of tampering, directing them to Ledger's published safety instructions.
Physical supply chain tampering is a risk for the whole industry. We are reviewing the controls that apply to our direct sales and to resellers, and we will share what we can.
Pascal Gauthier, Ledger CEO
In a separate statement, Ledger CEO Pascal Gauthier acknowledged the broader implications of the attack and outlined the company's response. Gauthier indicated that Ledger intends to examine its chain-of-custody procedures and tamper-detection mechanisms across both direct sales operations and third-party reseller networks. The company has also extended an invitation to security researchers and competing vendors to participate in assessing and strengthening these protective measures.